
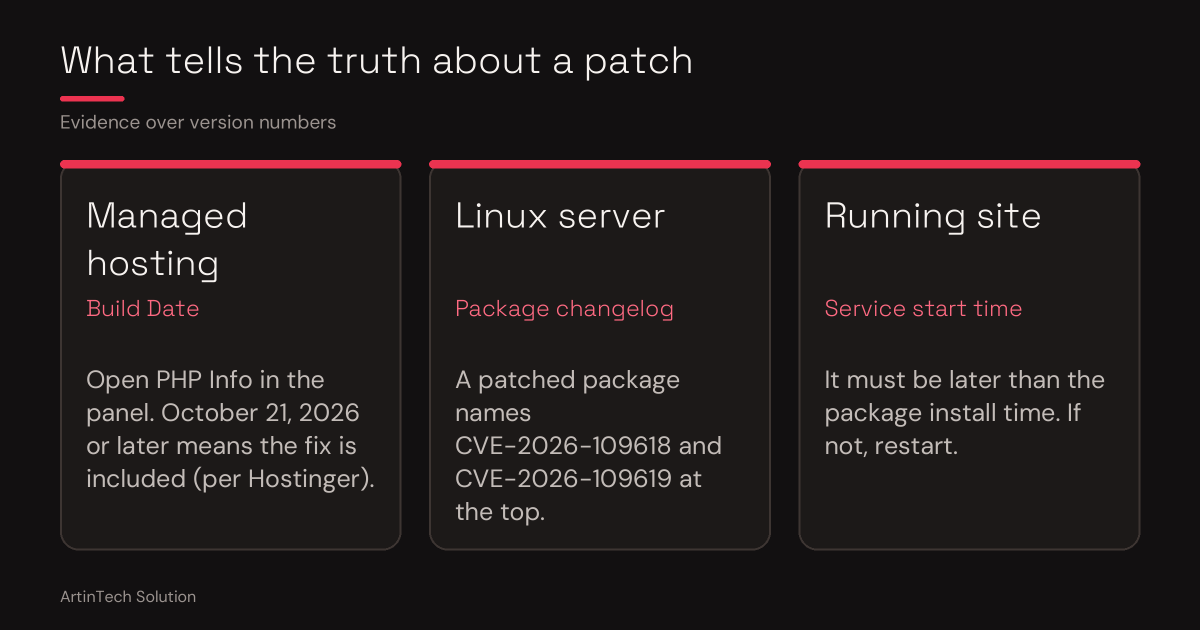
On managed hosting, the security fix for CVE-2026-109618 and CVE-2026-109619 can go inside your existing PHP version. Your site can show PHP 8.2.34 and still be patched. So the version number cannot tell you whether you are safe. The build date can.
Check the build date on Hostinger
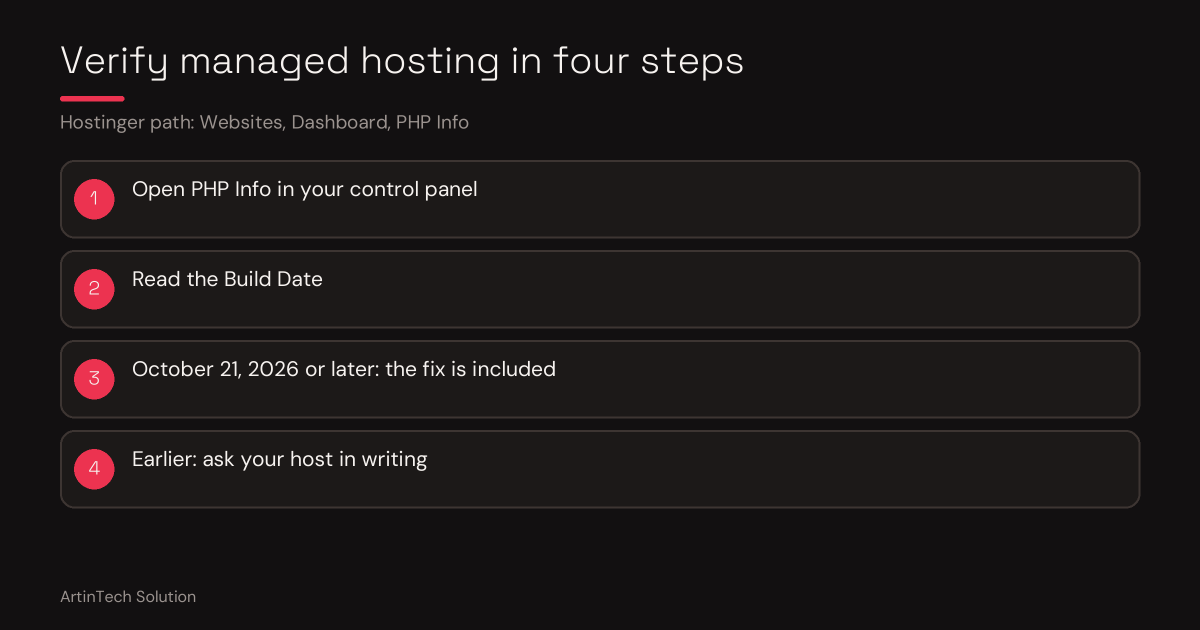
Hostinger's guidance is to open Websites, then Dashboard, then PHP Info in the control panel and read the Build Date. A build date of October 21, 2026 or later means the fix is included. Hostinger says it completed the rollout across all hosting plans except VPS on October 22.
Checking on cPanel and other hosts
CPanel hosts differ: each provider patches on its own schedule and the panel layout varies. The reliable approach is the same. Look for the PHP build date where your host exposes it, and ask your provider in writing whether the fix for CVE-2026-109618 and CVE-2026-109619 is included in the PHP build your account uses. Hosts can answer from their own changelogs.
Never create a public phpinfo page to check
A public phpinfo() file shows your server's internals to anyone. Use the panel's built-in PHP Info page instead, and delete any file you create the moment you are done.
Then move to a supported PHP version
Patched does not mean future-proof. PHP 8.2 official security support ends on December 31, 2026, and PHP 8.4 is supported until the end of 2028. A safe upgrade path looks like this:
- Take a full backup
- Update your CMS, themes and plugins
- Test on a staging copy for larger sites
- Switch the PHP version in the panel
- Test the site and read the PHP error log
After moving to PHP 8.4 you may see deprecation warnings such as implicitly nullable parameter types. The site keeps running, but the code should be fixed before a future PHP version rejects it.
// Before: deprecated in PHP 8.4
function findOrders(string $status = null) {}

// After
function findOrders(?string $status = null) {}
When to hand it to ArtinTech Solution
- Your plugins or custom code break on a newer PHP
- You run a store or booking system and cannot risk downtime
- Your host cannot confirm the fix
- You want a written confirmation of what is patched and what is not
We verify the patch state, test the upgrade on staging, fix compatibility problems and switch you over. See our WordPress and custom development services.
Legacy PHP code on managed hosting? Hire ArtinTech Solution experts today for professional security audits, PHP upgrades, and emergency fixes.