Two servers, two scary numbers. A hosting account shows PHP 8.2.34 while the fix shipped in 8.2.35. A VPS reports 8.3.6 while the fix is in 8.3.36. Both look unpatched. Both can be fully patched.
Why the number lies: backporting
Hosting companies and Linux distributions such as Ubuntu and Debian often put a security fix inside an older version number instead of bumping it. That practice is called backporting. An old number alone does not mean a server is vulnerable.
The other direction: new files, old workers
Updating a package puts new PHP files on disk, but PHP-FPM workers that were already running keep the old code in memory until the service restarts. Your terminal can show a patched build while your website still runs the vulnerable one.
Three versions of PHP on one server
- PHP CLI: what
php -vprints in a terminal - PHP-FPM, the web server's PHP: what actually serves your site
- Workers already in memory: old code until they are restarted

What tells the truth instead
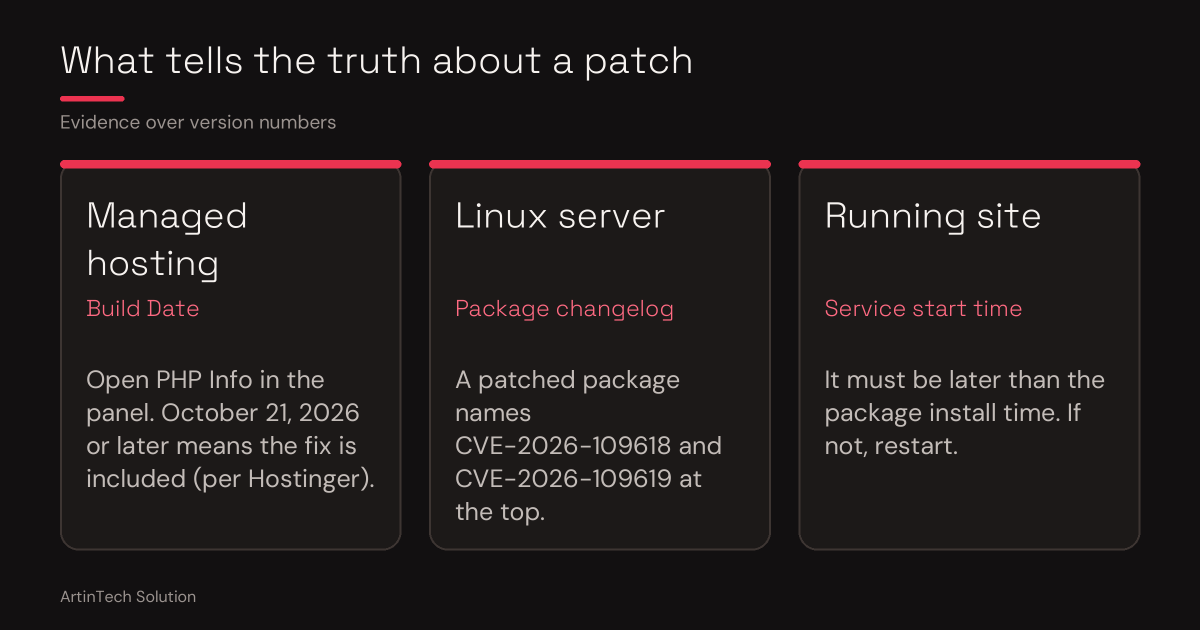
- Managed hosting: the Build Date on the PHP Info page. Hostinger says October 21, 2026 or later means the fix is included.
- Linux servers: the package changelog, which names the CVEs fixed.
- Running workers: compare the package install time with the service start time.
zcat /usr/share/doc/php8.3-fpm/changelog.Debian.gz | head -4
grep php8.3-fpm /var/log/dpkg.log | tail
systemctl status php8.3-fpm
On Linux servers the PHP project gave major distributions the patch before the public release, so a build date earlier than October 21 can still be a patched package. The changelog is the proof.
Why this is worth paying an expert for
Reading these signals correctly takes experience, and a wrong call leaves you either panicking over a safe server or trusting an exposed one. ArtinTech Solution verifies the real patch state of your hosting account or VPS from evidence, and tells you in plain language what needs fixing.
Not sure which number to trust? Hire ArtinTech Solution experts today for professional security audits, PHP upgrades, and emergency fixes.